Category .NET
Using Azure Cognitive Search Suggesters in ASP.NET Core and Autocomplete
This post shows how to implement an autocomplete in an ASP.NET Core Razor Page using Azure Cognitive Search Suggesters. Code: https://github.com/damienbod/AspNetCoreAzureSearch Posts in this series Implement a full text search using Azure Cognitive Search in ASP.NET Core Using Azure Cognitive Search Suggesters in ASP.NET Core and Autocomplete Implement a Blazor full text search using Azure […]
Using encrypted access tokens in Azure with Microsoft.Identity.Web and Azure App registrations
This post shows how to use encrypted access tokens with Microsoft Entra ID App registrations using Microsoft.Identity.Web. By using encrypted access tokens, only applications with access to the private key can decrypt the tokens. When using encrypted tokens, you can prevent access tokens data being used or read by such tools as https://jwt.ms or https://jwt.io […]
Implement a full text search using Azure Cognitive Search in ASP.NET Core
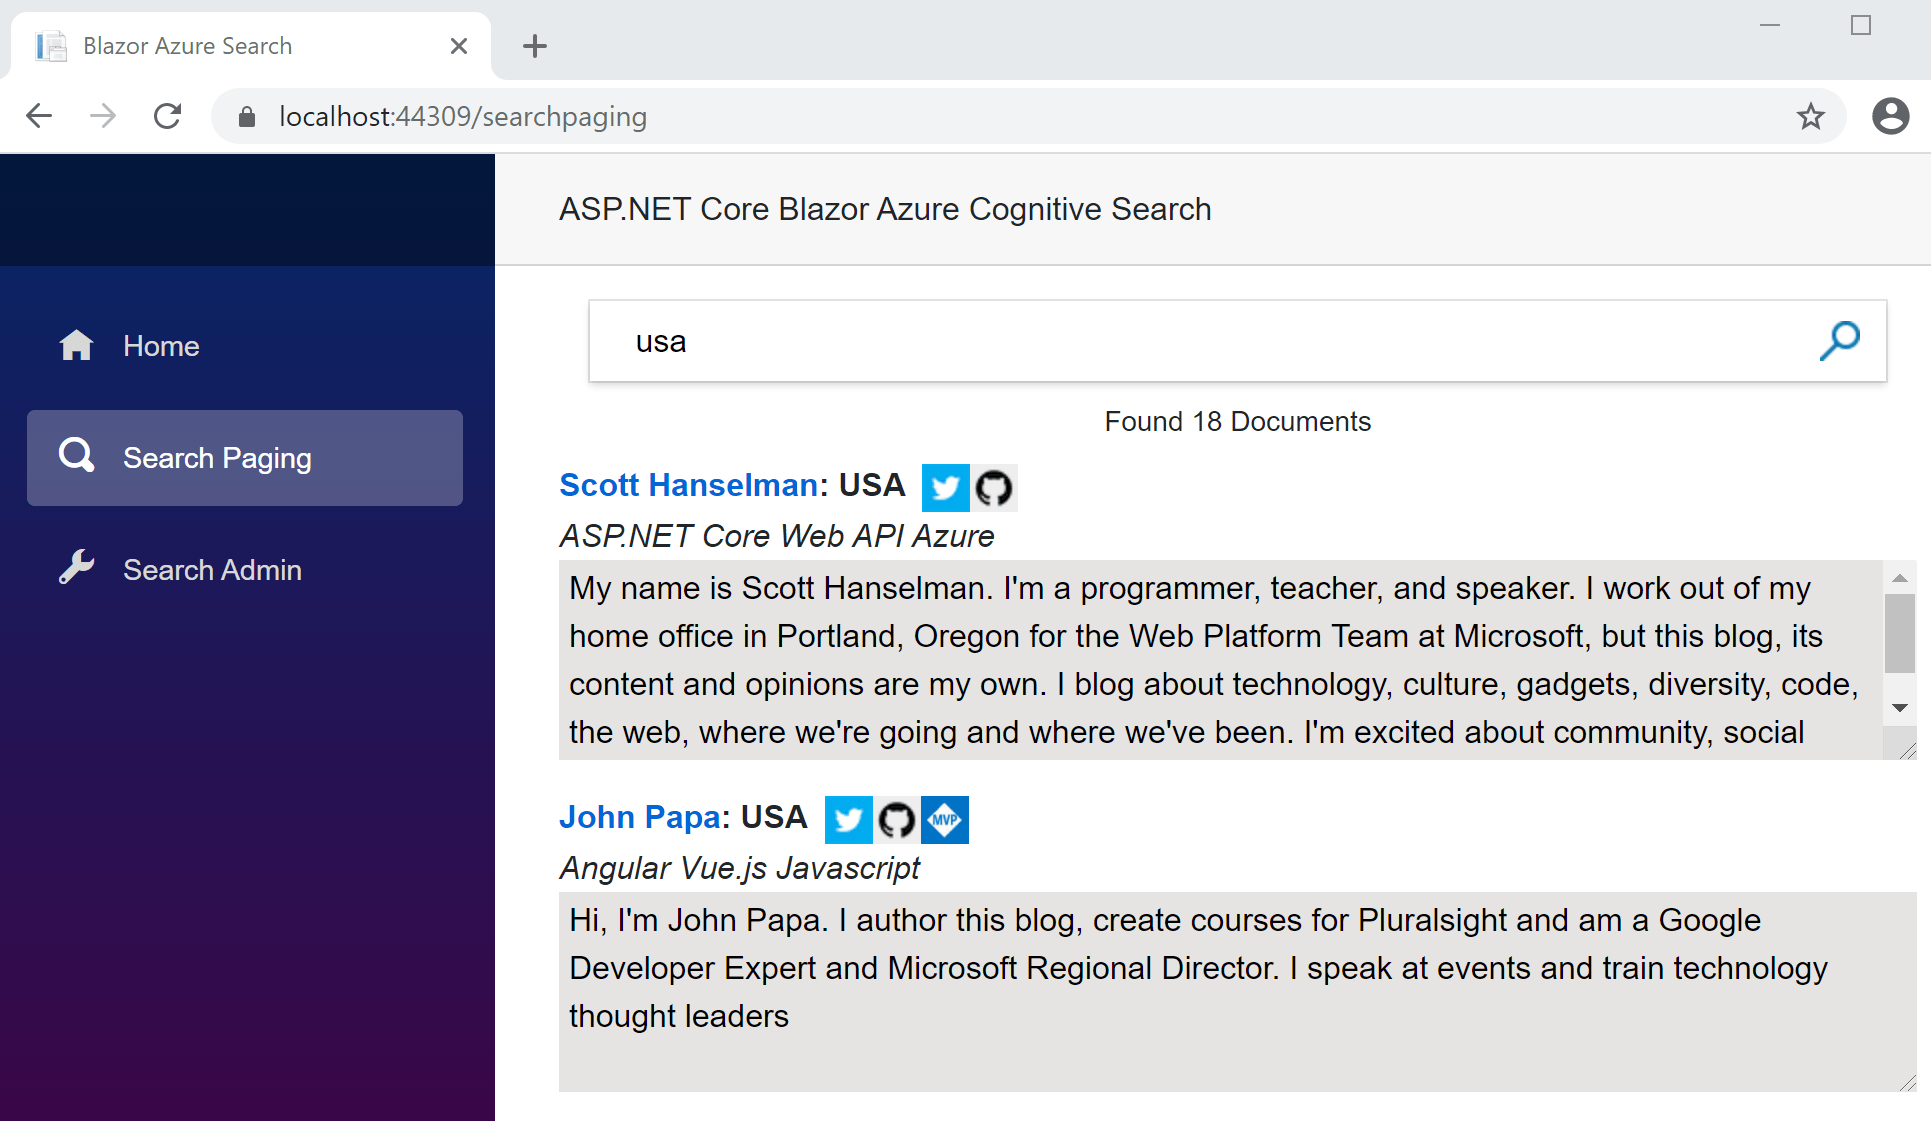
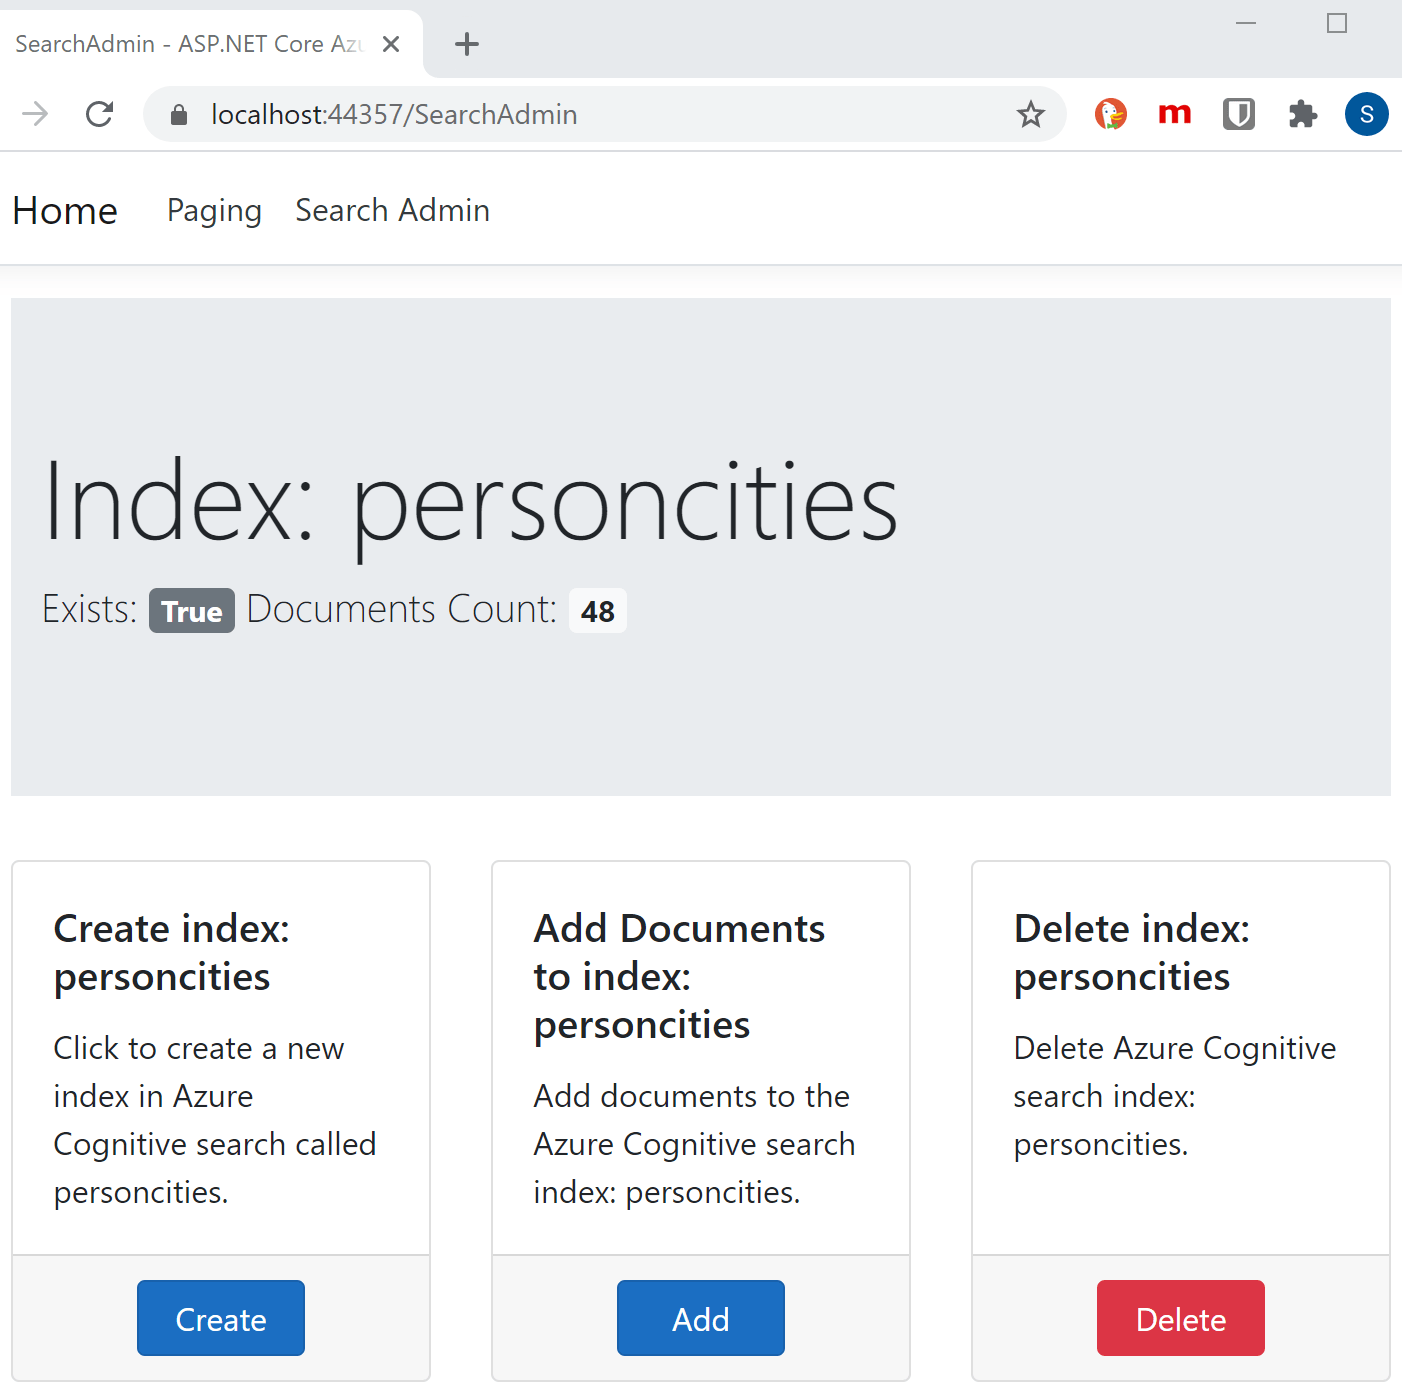
This article shows how to implement a full text search in ASP.NET Core using Azure Cognitive Search. The search results are returned using paging and the search index can be created, deleted from an ASP.NET Core Razor Page UI. Code: https://github.com/damienbod/AspNetCoreAzureSearch Posts in this series Implement a full text search using Azure Cognitive Search in […]

Using Key Vault certificates with Microsoft.Identity.Web and ASP.NET Core applications
This post shows how Azure Key Vault certificates can be used with Microsoft.Identity.Web in an ASP.NET Core application which requires a downstream “access_as_user” API. The Microsoft Entra ID App Registrations requires a certificate instead of a client secret. Code: https://github.com/damienbod/MicrosoftEntraIDAuthMicrosoftIdentityWeb Posts in this series History 2023-11-28 Updated to .NET 8 Creating the Key Vault certificates […]
Implement Microsoft Entra ID Client credentials flow using Client Certificates for service APIs
This post shows how to implement an Microsoft Entra ID client credential flows to access an API for a service-to-service connection. No user is involved in this flow. A client certificate (Private Key JWT authentication) is used to get the access token and the token is used to access the API which is then used […]

Securing Azure Functions using ME-ID JWT Bearer token authentication for user access tokens
This post shows how to implement OAuth security for an Azure Function using user-access JWT Bearer tokens created using Microsoft Entra ID and App registrations. A client web application implemented in ASP.NET Core is used to authenticate and the access token created for the identity is used to access the API implemented using Azure Functions. […]
Securing Azure Key Vault inside a VNET and using from an Azure Function
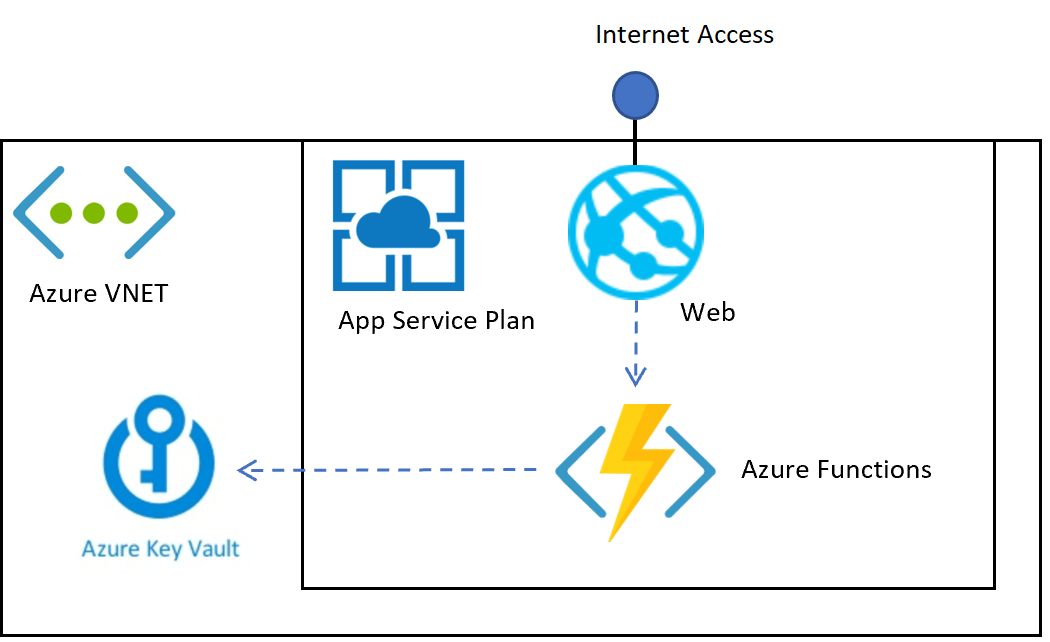
This post shows how an Azure Key Vault can be protected inside an Azure virtual network. The deployment is setup so that only applications in the same VNET can access the Key Vault. To implement this, the access to the Key Vault is restricted to the VNET and secondly, the applications accessing the Key Vault […]
Encrypting texts for an Identity in ASP.NET Core Razor Pages using AES and RSA
The article shows how encrypted texts can be created for specific users in an ASP.NET Core Razor page application. Symmetric encryption is used to encrypt the text or the payload. Asymmetric encryption is used to encrypt the AES key and the IV of the symmetric encryptions. Each ASP.NET Core Identity has an associated X509Certificate2 with […]
Symmetric and Asymmetric Encryption in .NET Core
This post looks at symmetric and asymmetric encryption and how this could be implemented in .NET Core. Symmetric encryption is fast and can encrypt or decrypt large amounts of text, streams or files but requires a shared key. Asymmetric encryption can be used without shared a key, but can only encrypt or decrypt small texts […]
Securing Azure Functions using API Keys
This article shows how to secure Azure Functions using API Keys. This is useful, if you have no control over the API client implementation, the client code base cannot be easily changed or the client is not Azure hosted. This should only be used with trusted clients and is for machine to machine usage. Code: […]

 Software Engineering
